Old Fucking Punk @lwriemen@librem.one
#ShlaerMellor, #FunctionPointAnalysis, #punk, #environmentalist, #unionAdvocate, #anarchosocialist
"with a big old lie and a flag and a pie and a mom and a bible most folks are just liable to buy any line, any place, any time" - Frank Zappa
Joined May 2019
Old Fucking Punk
boosted

#Apple Doesn’t Want You to Worry About the New #Apple Watch's Listening Features
The new #AppleWatch includes several “intelligent” listening features that have #privacy and #security baked in. But the protections can’t change the facts of what the tools do.
Old Fucking Punk
boosted
California is deciding who may verify AI, and one investigation already cost $400,000 in tokens - https://thenextweb.com/news/california-sb-813-independent-verification-organisations-metr-400000-tokens-openai-paid-eu-ai-act-scientific-panel-article-68 "#OpenAI supplied the credits that paid for the inquiry into its own agents, while Europe appointed 60 independent experts in June"
Old Fucking Punk
boosted
The Problem with Intellectual Property - https://c4sif.org/2026/09/the-problem-with-intellectual-property-springer-2026/ "explores the nature of property rights and argues that IP is incompatible with genuine private property rights, liberty, and justice, and distorts and impedes artistic creation and innovation." #intellectualmonopolies
Old Fucking Punk
boosted
US government argues that fair use applies to #OpenAI’s training of #LLMs in key #copyright case - https://walledculture.org/us-government-argues-that-fair-use-applies-to-openais-training-of-llms-in-key-copyright-case/
Old Fucking Punk
boosted

#Forgejo 16.0.4 and 15.0.8 were just released! They are critical security releases.
We recommend that all installations are upgraded to the latest version as soon as possible.
Check out the release notes and download it at https://forgejo.org/releases/. If you experience any issues with this release, please report to https://codeberg.org/forgejo/forgejo/issues.
Old Fucking Punk
boosted

@ambiguous_yelp @Xtreix @rhelune
From what I read, they were talking about doing LLM-based code review, not code authoring. This involves a different set of problems, which are more subtly.
They acknowledged that the LLMs produced a lot of inaccurate and misleading feedback, but claimed that the good reports in the middle made this an acceptable tradeoff. This would be true, if developer time were unbounded.
The problem is, with the available effort, you are never going to be able to eliminate all bugs during code review. Even if you do formal verification, you only avoid bugs that aren't present in your specification and your specification complexity is such that it's pretty much guaranteed to contain bugs.
Even if you ignore the ethical issues surrounding LLMs, introducing a tool with a high false-positive rate into code review comes with a number of problems:
It distracts attention away from addressing feedback from deterministic tooling. Or, if your commits are gated on these, you move time away from fixing backlog bugs to reviewing the output from the LLM to find the things that aren't false positives.
It means human code reviewers will pay less attention, because there are already a lot of comments and some of them will be ones humans want to do.
It causes people to ignore the real bugs that it finds because they're hidden in the middle of false positives. We saw this 20 years earlier with Coverity: it found real bugs, but it also found a lot of not-actually-bug things. We recently found a bug in a certified MISRA C component that was hidden because someone had explicitly silenced the static analyser warning about it because they thought it was a false positive. The more common false positives are, the more likely people are to miss the real ones.
And all of that adds up to a project that doesn't think it has a duty of care to its users. And that's fine, unless you're a project that's telling everyone to switch to you because of security.
Old Fucking Punk
boosted

@Xtreix @rhelune allowing LLM contributions invites security holes - legitimizes the environment,culture&reality destroying surveillancec machine that is generative AI. And it encourages deskilling of an entire generation of security researchers ultimately placing all the security work (and trust associated with it) in the hands of the richest companies on the planet. I use FLOSS to escape the control of these people.
#LLM #LargeLyingMachine #GenAI #AISlop #VibeCoding #FLOSS #GrapheneOS
Old Fucking Punk
boosted

@zzt And if your own project is pro AI and pro cryptocurrency the slop pit that is github will still be happy to have you.
Old Fucking Punk
boosted

grapheneOS is now falsely claiming to be affected by the codeberg ban on cryptocurrency projects because they take donations in monero
of course these shitheads have a problem with codeberg banning slop and cryptocurrency projects, why wouldn’t they
Old Fucking Punk
boosted

I was just reflecting this morning on the push to integrate LLMs into the software development process. Thanks to LLMs, everything now is much more expensive (devices, energy, food), as well as the code. Every unit of code now costs many multiples of what it used to, and there is more of it.
Old Fucking Punk
boosted
@ambiguous_yelp They proudly tooted about starting LLM reviews the day before yesterday. That caused an outrage because why use GrapheneOS at all if you don't care about security?! Can't point you to it because I'm blocked. Can anyone else help?
Old Fucking Punk
boosted

My AI policy is "I don’t want any kind of interaction with that thing." And this should be all you need to know.
Old Fucking Punk
boosted
Graphene OS blocked me 😂
Old Fucking Punk
boosted
“I Don’t Want to Interact With Stochastic Parrots”
https://ploum.net/2026-09-09-ai_policy.html
> My AI policy is "I don’t want any kind of interaction with that thing." And this should be all you need to know.
This.
Old Fucking Punk
boosted
The “AI” doom narrative is really getting some traction this time around. Both got extensive coverage in Icelandic media and I’m seeing it spread far and wide among the web’s pseudo-intelligentsia. “Oh, no! These people know what they’re talking about so it must be true!”
It’s exhausting

Old Fucking Punk
boosted

RE: https://mastodon.social/@ryanprior/117243267025218934
Apparently, fascists took it personally when GNOME and Flatpak declined a sponsorship by Framework who previously donated to DHH's Omarchy.
That rejection is apparently why other fascists withdrew their sponsorships of GNOME and Flatpak in solidarity with Framework, and are spitefully funding Omarchy instead.
DigitalOcean is one of these fascist-lead companies.
Old Fucking Punk
boosted

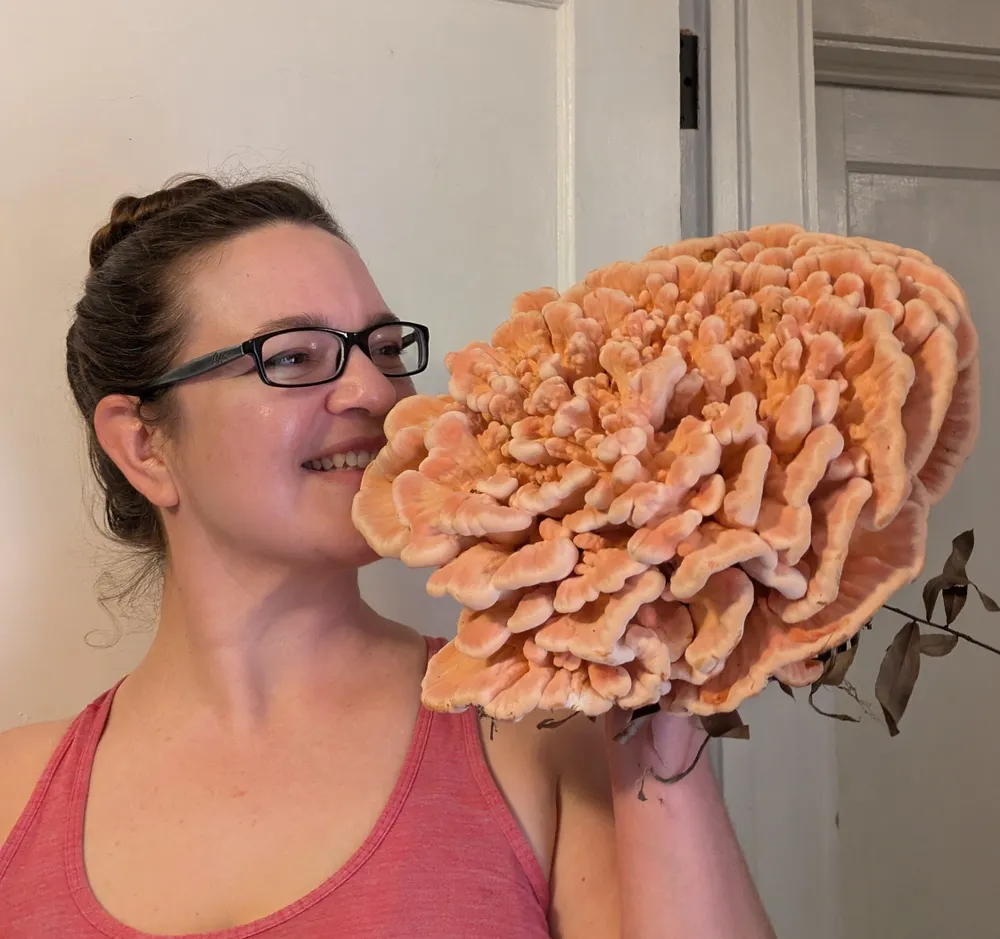
Anybody know what to do with FIVE POUNDS of chicken of the woods
Old Fucking Punk
boosted
RE: https://mastodon.social/@inthesetimes/117241440161419146
The nearest we have to this in San Francisco is the 2018 "Our City Our Home" fund. The Mayor's office recently persuaded the Supes to spend some of that fund on shelters instead of housing; the Supervisors knocked the fund's main creator off its board; and Proposition A on our upcoming Nov. 3, 2026 ballot would make it easier to crumple or end the board in future.
Cities can make good things. It's possible. But SF's centrist/conservative elected majority doesn't share that hope.
Old Fucking Punk
boosted
if you’re taking apple’s word on the obvious surveillance features because you liked their marketing: I’m concerned about the health of your frontal lobe
#ShlaerMellor, #FunctionPointAnalysis, #punk, #environmentalist, #unionAdvocate, #anarchosocialist
"with a big old lie and a flag and a pie and a mom and a bible most folks are just liable to buy any line, any place, any time" - Frank Zappa
Joined May 2019