Old Fucking Punk @lwriemen@librem.one
#ShlaerMellor, #FunctionPointAnalysis, #punk, #environmentalist, #unionAdvocate, #anarchosocialist #freeSoftwareAdvocate #cooperativeLife #noLLMs
"with a big old lie and a flag and a pie and a mom and a bible most folks are just liable to buy any line, any place, any time" - Frank Zappa
Joined May 2019
Old Fucking Punk
boosted

The right-wing owners of Scientific American, once the pillar of science writing, have ruined the publication's content and reputation. An incredibly sad situation: https://www.thenation.com/article/society/scientific-american-springer-nature-trump/
Old Fucking Punk
boosted
RE: https://narrativ.es/@janl/117484474907395355
#FOSDEM will not have a DEIB room 😔 True to #DIY #OpenSource spirit we will fix this ourselves.
Support @Gina @elena @RosannaSibora initial proposal for a DEIB room with the #FOSDEMPledge @janl proposes:
Take a min or 2 to discuss the need for diversity, equity, inclusivism & belonging (DEIB) in your talk or have a talk on this topic in the room you organise.
For me #FLOSS is about people. Let's make sure everyone feels welcome & enable their participation in the FLOSS ecosystem. ✊
Old Fucking Punk
boosted
I bought something from Best Buy online for store pickup, and they put me on a mail list that has no unsubscribe link. They want me to create an account to unsubscribe. I tried the chatbot with ridiculous results: It only wants to talk about products.
Spam filter time...
Old Fucking Punk
boosted
I work in the #food industry – and the UK is heading for full supply-chain collapse - https://www.thebureauinvestigates.com/stories/2026-10-21/food-industry-supply-chain-collapse-secret-source "#Climatechange will soon throw our food system into chaos. But solutions are there for a government willing to see them"
Old Fucking Punk
boosted
You can feel the AI in everything as a dev because every app and service you use is randomly broken far more frequently. You know that it's because code reviews and QA got thrown into the trash because you've had those meetings too.
Old Fucking Punk
boosted

@tehstu @baldur because Wiz didn't release their exploit, others are trying to reproduce it, and you can find lots of attempts on github under names related to 'php2shell'. Elias surveyed *those*, and claims that none of *those* actually works as an exploit against a server without specific non-default properties.
Elias' contention is that reproducing an exploit like Wiz's for this is non-trivial - much harder than other 'famous' vulnerabilities - and nobody has done it yet.
Old Fucking Punk
boosted
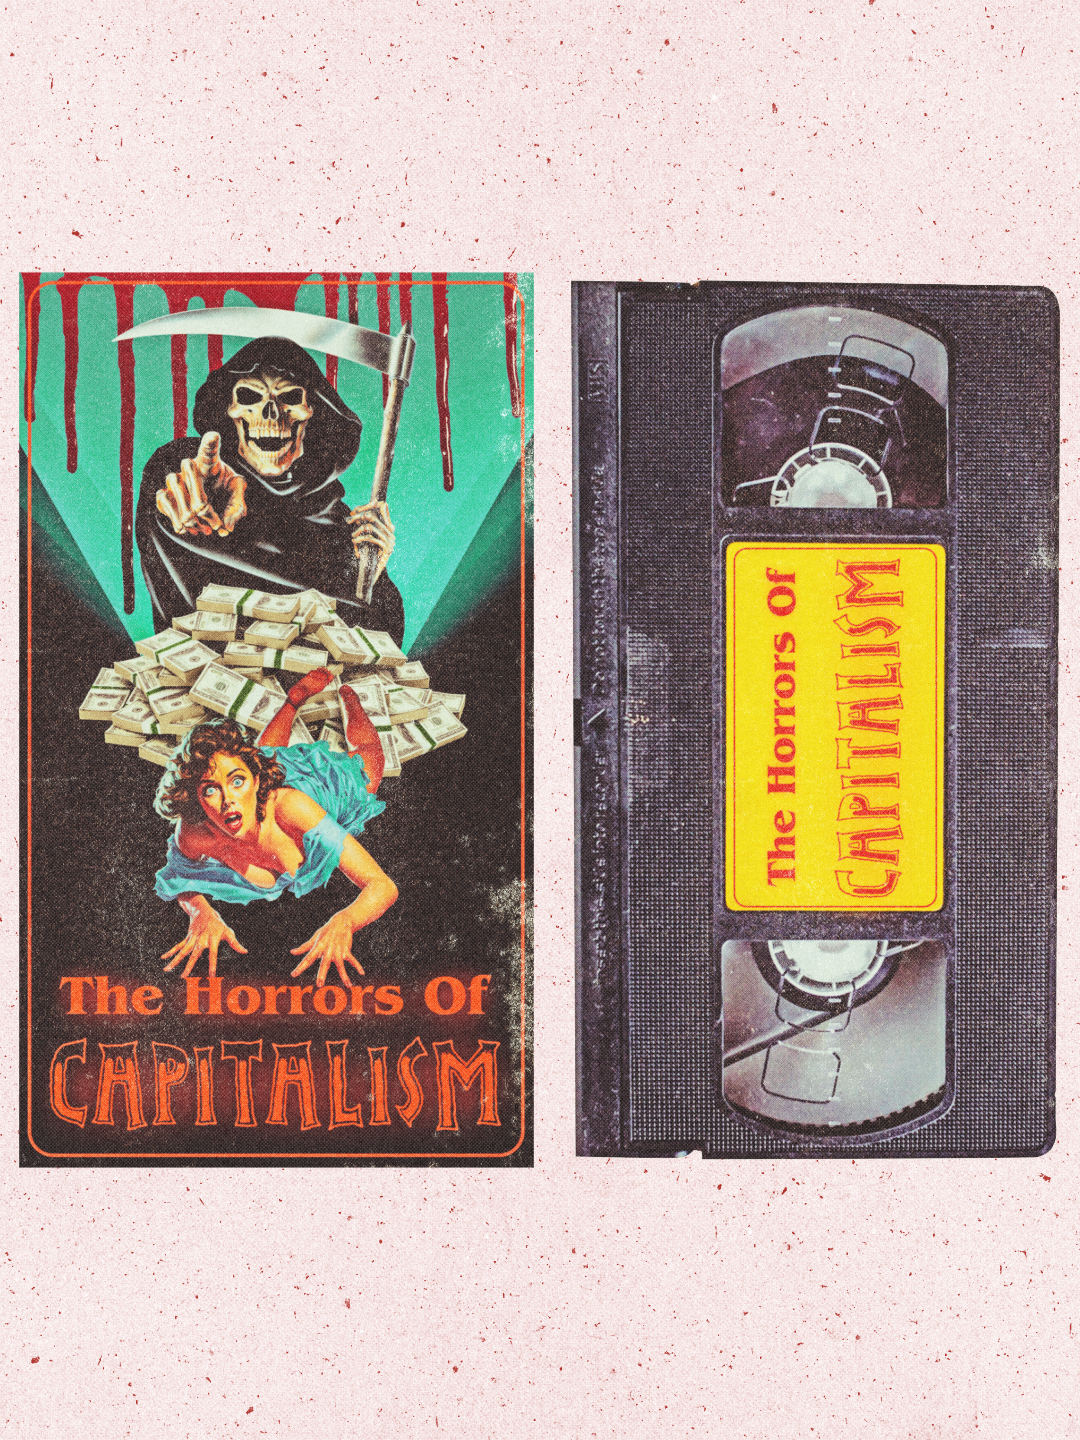
What's scarier than life under capitalism?
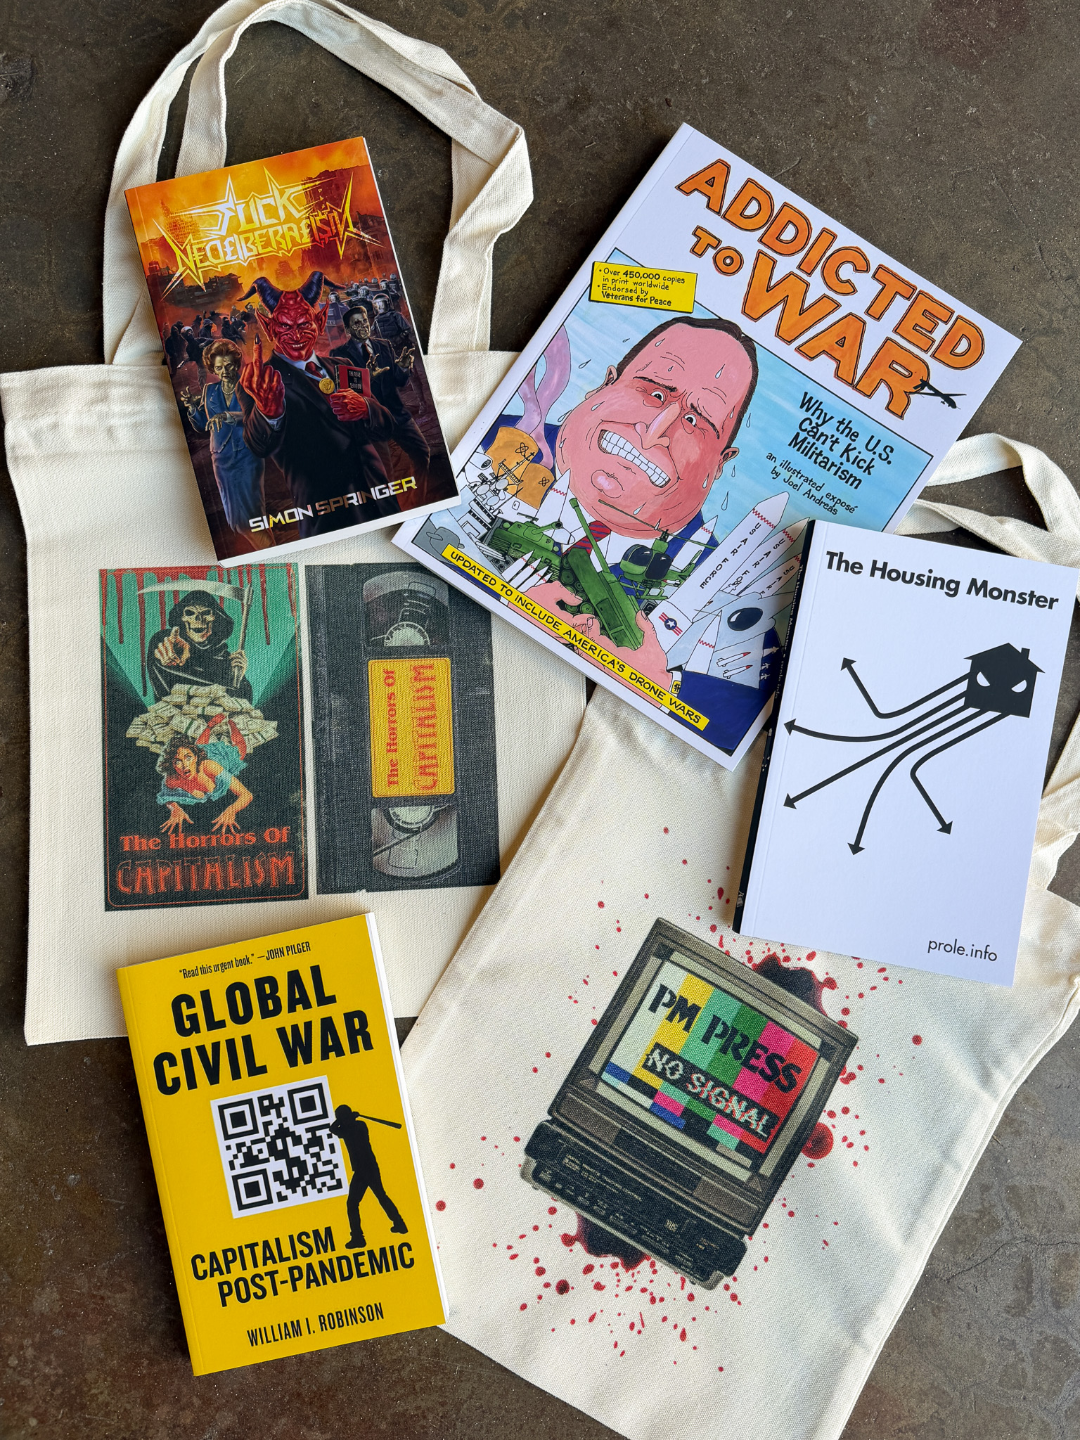
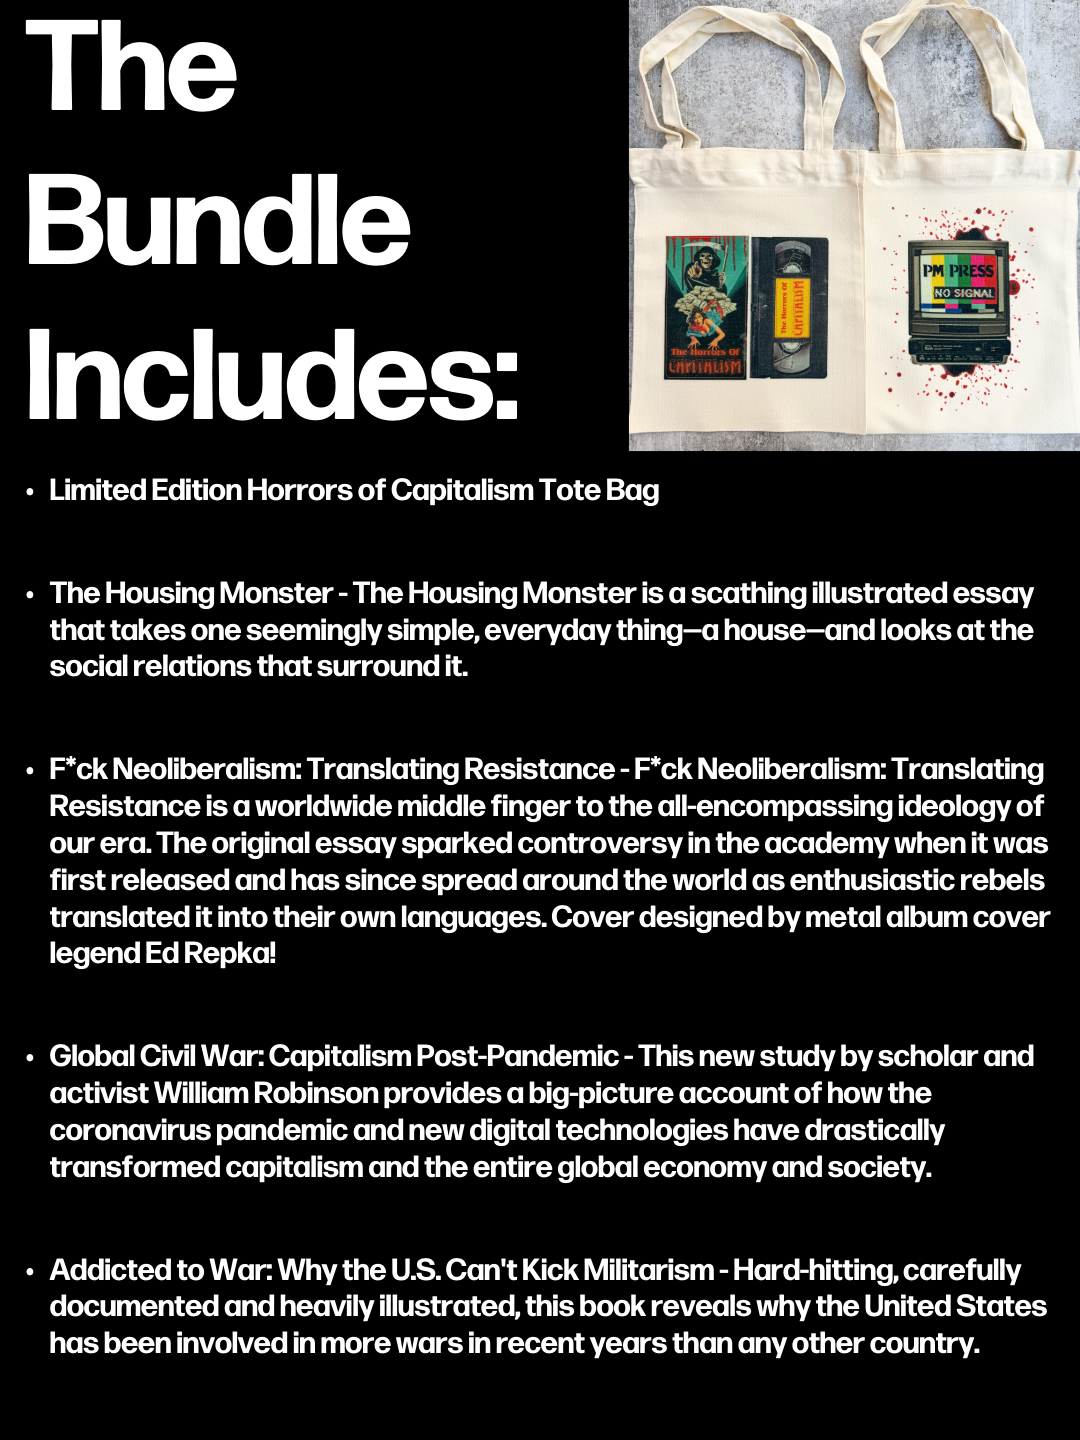
This limited tote bag and book bundle includes our Horrors of Capitalism tote plus four books examining, critiquing, and laying bare just a few of the horrors we face daily living under late-stage capitalism. Get these 4 books and the limited edition tote thru 11/1 here: https://www.pmpress.org/product/the-horrors-of-capitalism-tote-bag-and-book-bundle
#Capitalism has obviously changed how some common phrases are interpreted these days. https://infosec.exchange/@0xabad1dea/117485038136053872
The people agreeing with this assume the worker has little recourse to make their own choice of tools. Such an assumption didn't used to be common.
Old Fucking Punk
boosted

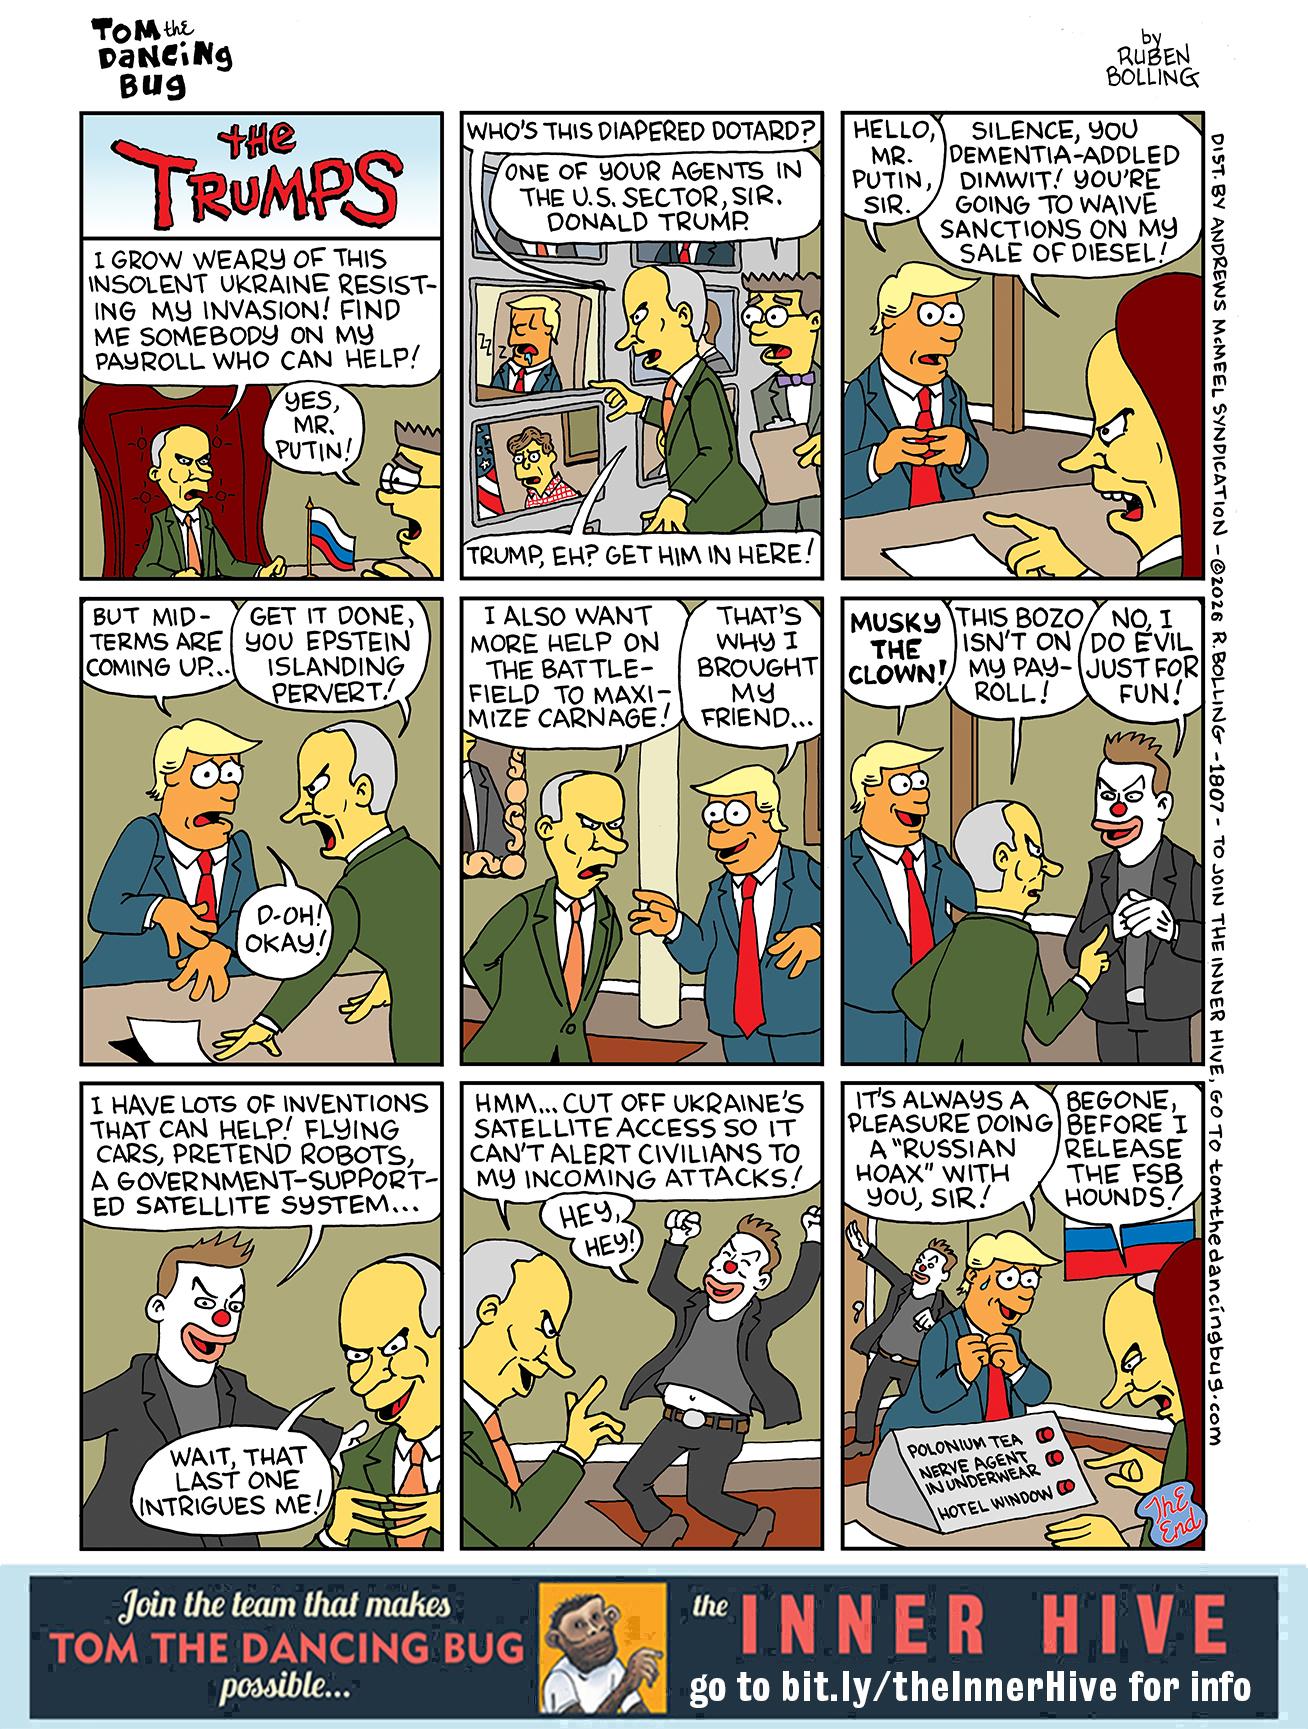
🔵 This week's Tom the Dancing Bug
🤡 D'oh! A Simpsonian look at Putin/Trump/Musk's Ukrainian War
-
Brought to you by the Inner Hive, including long-time member Auntie Freeze and new member Josh Finder! Join us at tomthedancingbug.com/the-inner-hive/
READ IT RIGHT HERE👇
Old Fucking Punk
boosted
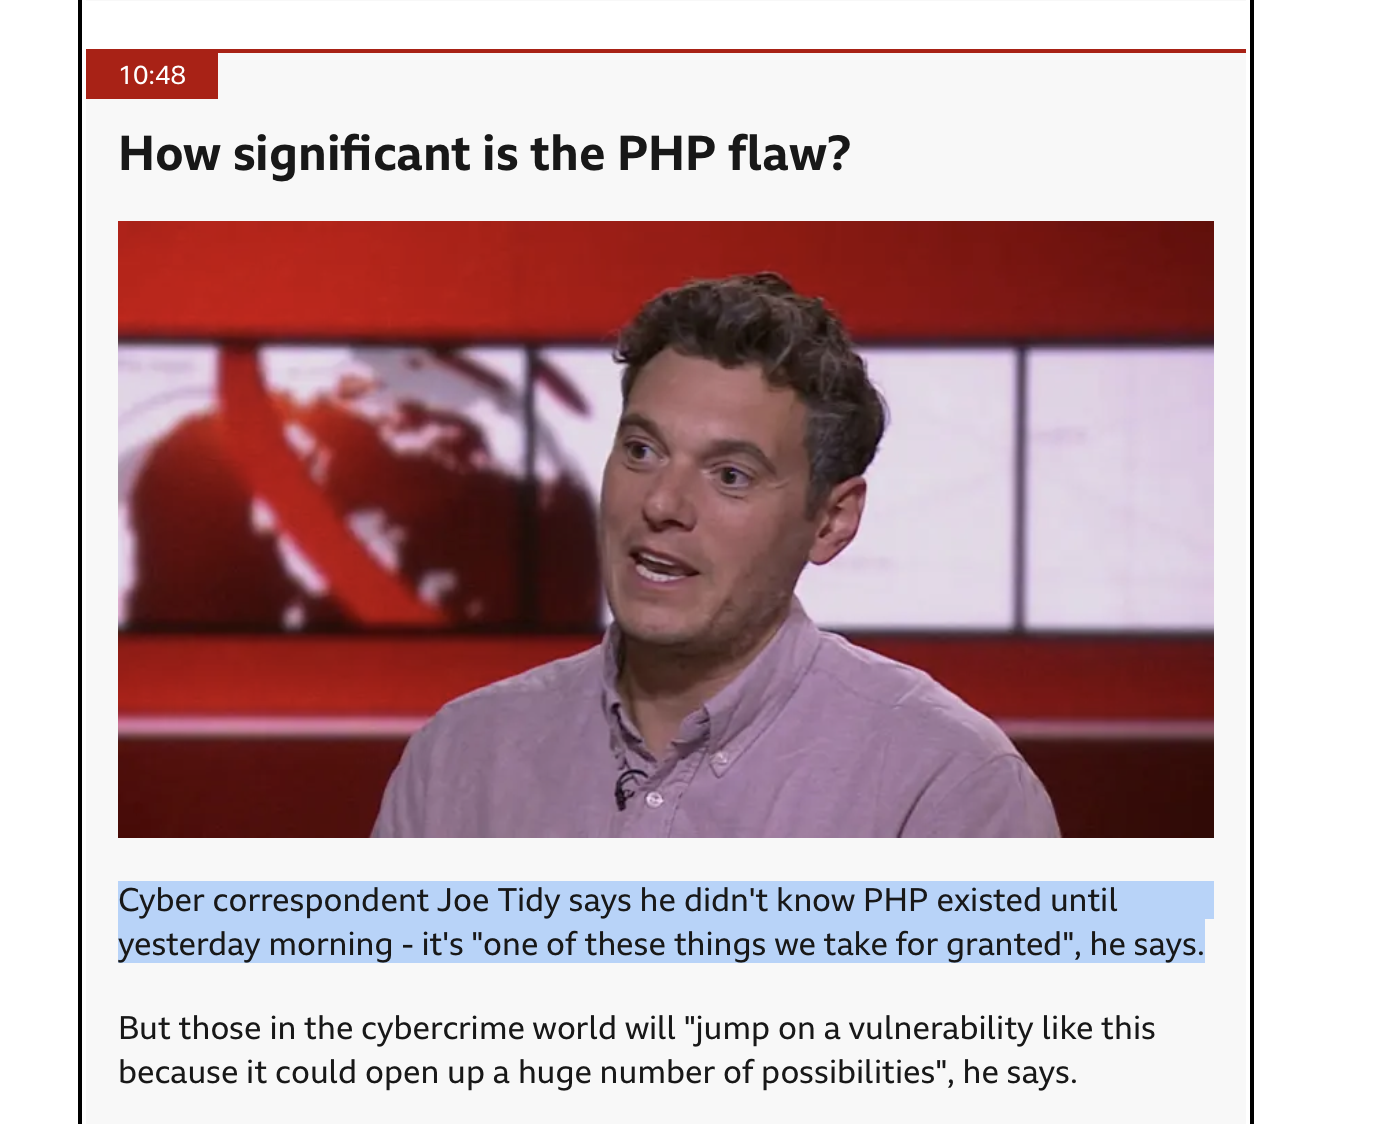
The BBC being absolutely on the button. Their Cyber correspondent had never even heard of php before? Really??? 🤦♀️
Old Fucking Punk
boosted
But my observation was primarily that many of the claims I've seen surface over the past day or so seem quite dubious in hindsight and seems to have led to a herd effect of sorts.
Having worked in corporate software environments for 30+ years, I'm used to seeing many offenses against good practice (release without adequate testing, adoption of tools and processes without supporting metrics, inadequate to no training, etc.), so why does this AI rollout seem particularily egregious? Maybe this will help explain: https://neuromatch.social/@jonny/117483555597964151
It does seem kind of funny that all these FOSS security breaches seem to always come from code hosted on #MicrosoftGitHub. It's almost like being in their repositories automatically makes your code more scrutinized by some large corporation that hates FOSS.
Old Fucking Punk
boosted
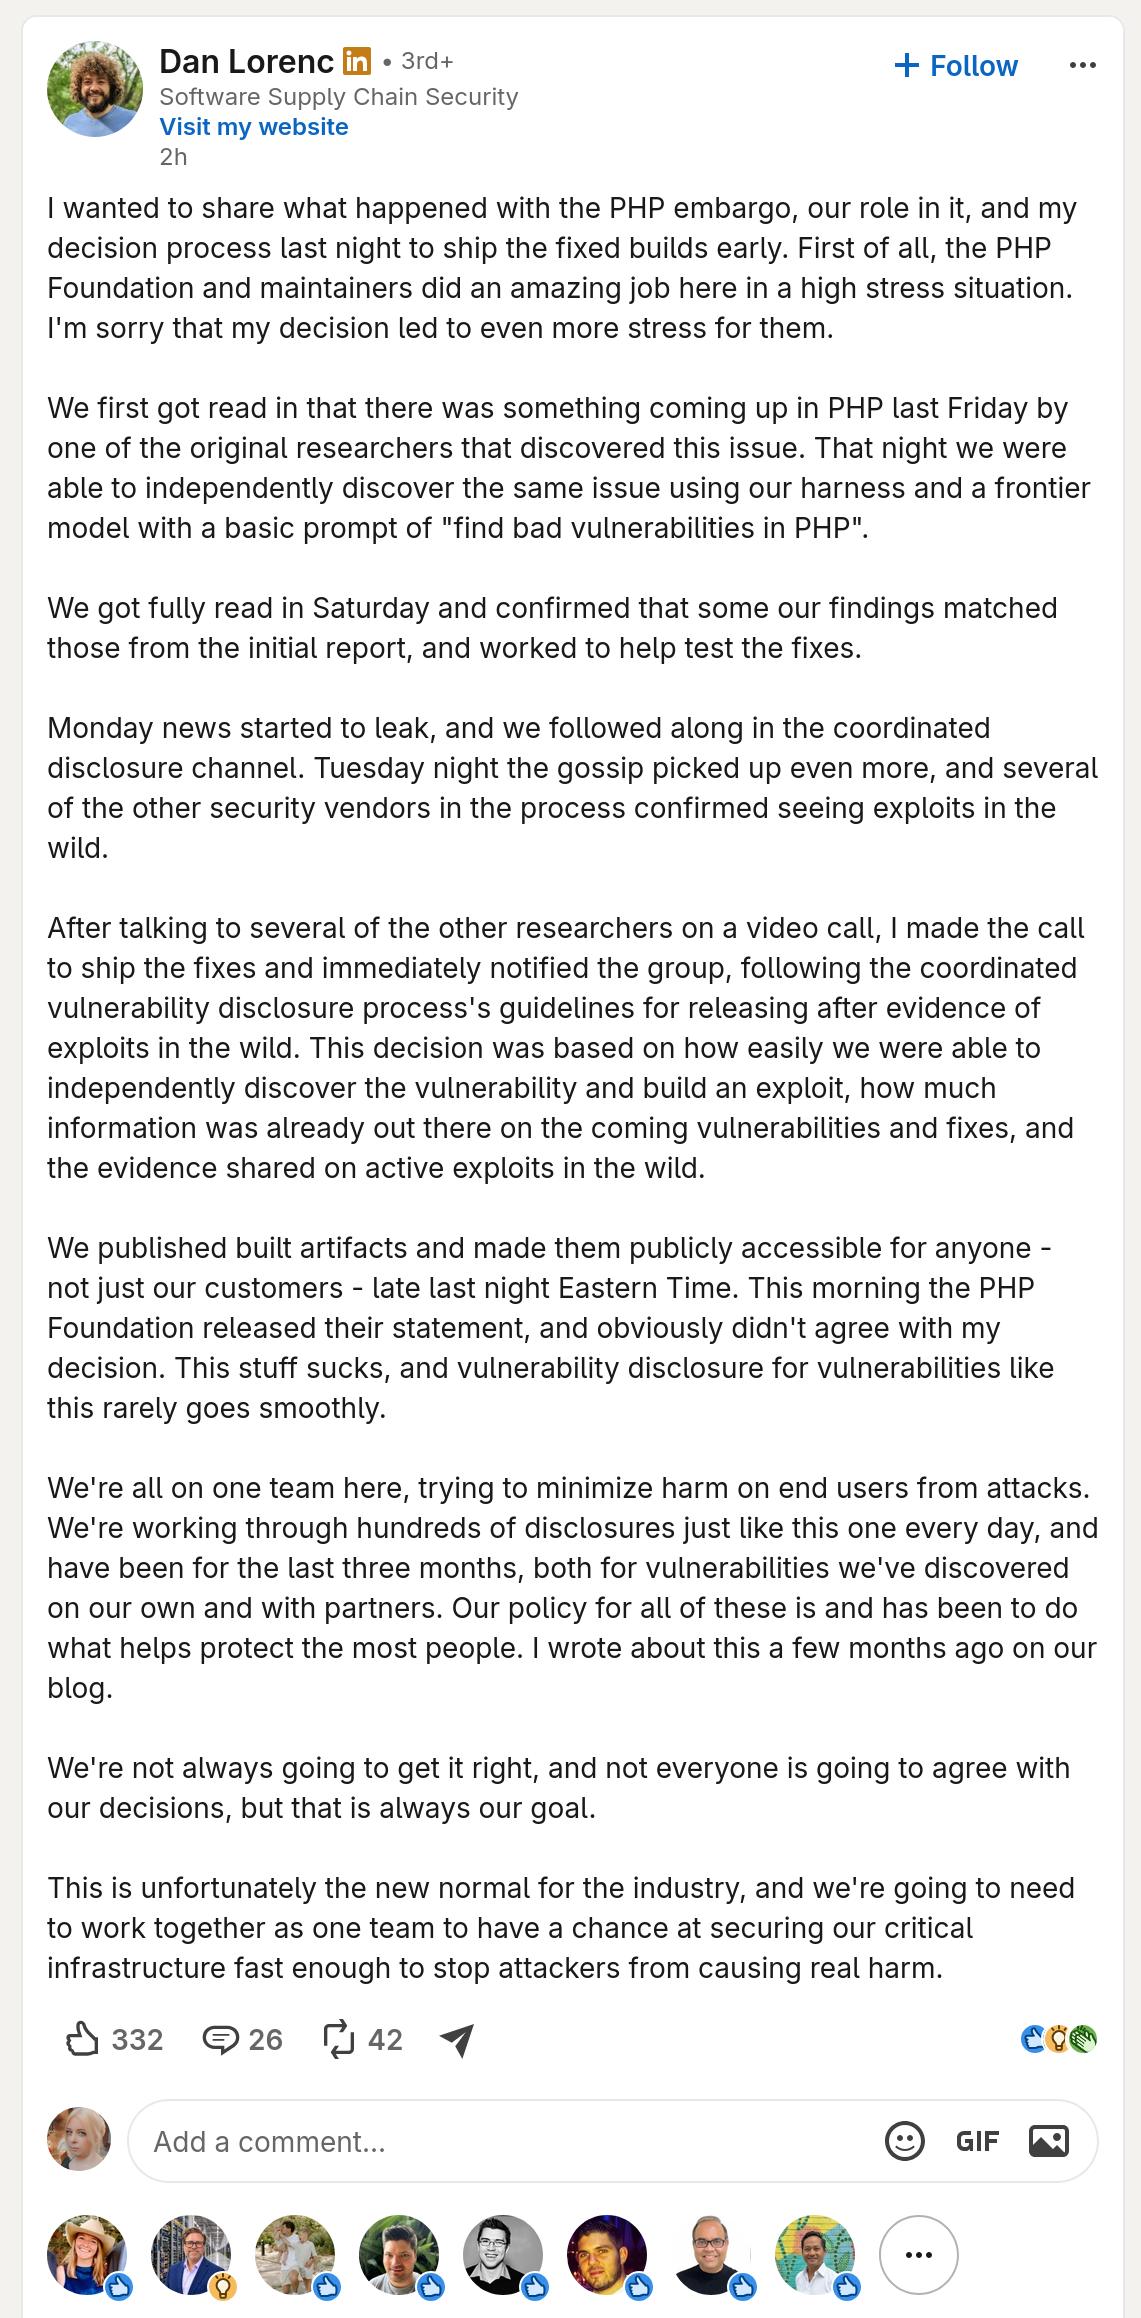
If this had been a woman in a senior dev, security or SRE position, she would not have concluded this with an inspiring LinkedIn post about "not always getting it right".
This guy is the CEO of Chainguard by the way.
I hope that this causes Chainguard to be kept away from any security related embargoes until trust has been properly restored.
Old Fucking Punk
boosted

RE: https://social.coop/@coopcloud/116770343059078681
Ever since yesterday's announcements of (oh so many) security vulnerabilities, our community has been hard at work identifying vulnerable recipes which need to be undeployed, writing checks and guides, and updating recipes as new images come in.
In today's Kite Flying (in just over an hour!) we'll be sharing our process and discussing recommendations for coop cloud deployments. See you there!
- amras <3
Old Fucking Punk
boosted
most test suites are actually not very fine constraints on the system under test; the idea that "any program that passes the tests is acceptable" is nonsense, even more so when you're also generating the test suite
Old Fucking Punk
boosted
RE: https://toot.cafe/@baldur/117484059424957991
The reason why the way many have been talking—describing “AI”-written exploits popping up require heroic defence—smells like bullshit is that, so far, all of the exploits seem to require pre-existing second vulnerabilities so bad that any site with them would have been hacked months ago already.
That can change any time, which is why you should patch PHP ASAP, but many of the responses smack of madness of crowds
Old Fucking Punk
boosted
But it really also does look like anybody describing waves of exploits targeting their site yesterday or heroic work by their "agents" to safeguard their servers may be operating on the reality-deficient side of the bullshit scale.
Old Fucking Punk
boosted
It's not only that the EUID wallet prefers iOS and Android, they don't want to even look at alternatives:
https://github.com/eu-digital-identity-wallet/.github/issues/20#issuecomment-6337434090
It's nice that the spec is open but that only helps so much as long as 💵 goes into the proprietary software channels.
Old Fucking Punk
boosted
RE: https://mastodon.social/@Edent/117483785620327786
“There isn't an easy exploit for this PHP vulnerability · Elias Taylor”
https://eliastaylor.com/noexploit/
> One really amusing thing in common with most of these "PoC"s is that they lean on "LFI", or local-file-inclusion, to make the vulnerability. In non-php terms, their exploit chain requires the server to already have a severe code-level vulnerability.
#ShlaerMellor, #FunctionPointAnalysis, #punk, #environmentalist, #unionAdvocate, #anarchosocialist #freeSoftwareAdvocate #cooperativeLife #noLLMs
"with a big old lie and a flag and a pie and a mom and a bible most folks are just liable to buy any line, any place, any time" - Frank Zappa
Joined May 2019